If someone may have accessed your business email, treat it as an incident rather than just an annoying password problem. Contact your organisation’s administrator through a trusted route and record what you have noticed.
Contain the access
An authorised administrator should follow Microsoft’s compromised-account process, which includes securing the account and reviewing active access. A password change alone may not address every session, permission or forwarding rule.
Review what changed
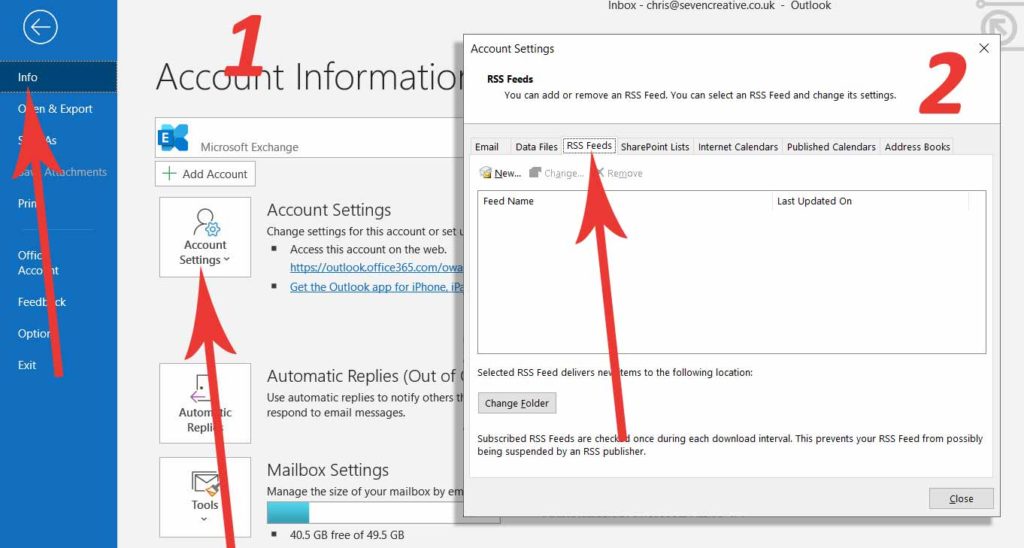
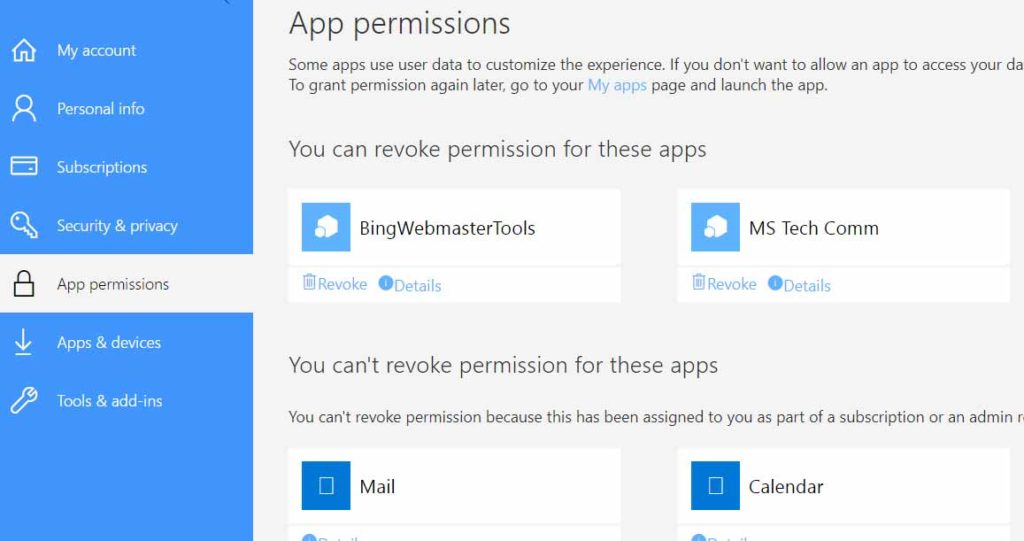
Check sign-in evidence, mailbox forwarding, inbox rules and application permissions. Look for unexpected changes to recovery or authentication methods. Keep relevant evidence privately; do not post message contents or customer information in a public support thread.
Assess messages and affected people
Use the available audit and message-trace tools within your authorised role. Work out whether unauthorised messages were sent or information was accessed. The organisation must decide what further communication or reporting is needed, based on the actual incident.
Improve the recovery position
Review multifactor authentication, approved applications and the cause of the compromise before assuming everything is secure. An absence of strange Sent Items is not proof that no messages were sent.
This is an initial orientation, not a complete incident-response procedure or a guarantee of recovery. See email security and deliverability for related configuration work, and involve the appropriate incident-response expertise where needed.
Sources and further reading
Guidance checked 26 October 2026: Microsoft’s compromised-account response guidance.
Illustrations